Make compliance continuous, not a sprint before every audit
Most compliance programs are built for audit day and drift out of compliance soon after. This guide shows how to build the operational foundation that keeps your device fleet compliant every day, and turns each new regulation into a mapping exercise instead of a fresh project.
What’s inside:
- Why the standard compliance model fails, from the pre-audit sprint to the restart problem with every new regulation
- The five operational domains behind device compliance, with the metric to track for each
- Four capabilities that make compliance continuous, and what auditors actually look for in your evidence
- Where regulatory pressure is heading, from NDAA 889 and NERC CIP to FCC device rules and the EU Cyber Resilience Act

HOW WE SOLVE IT
Device state mapped to the rules, recorded continuously.
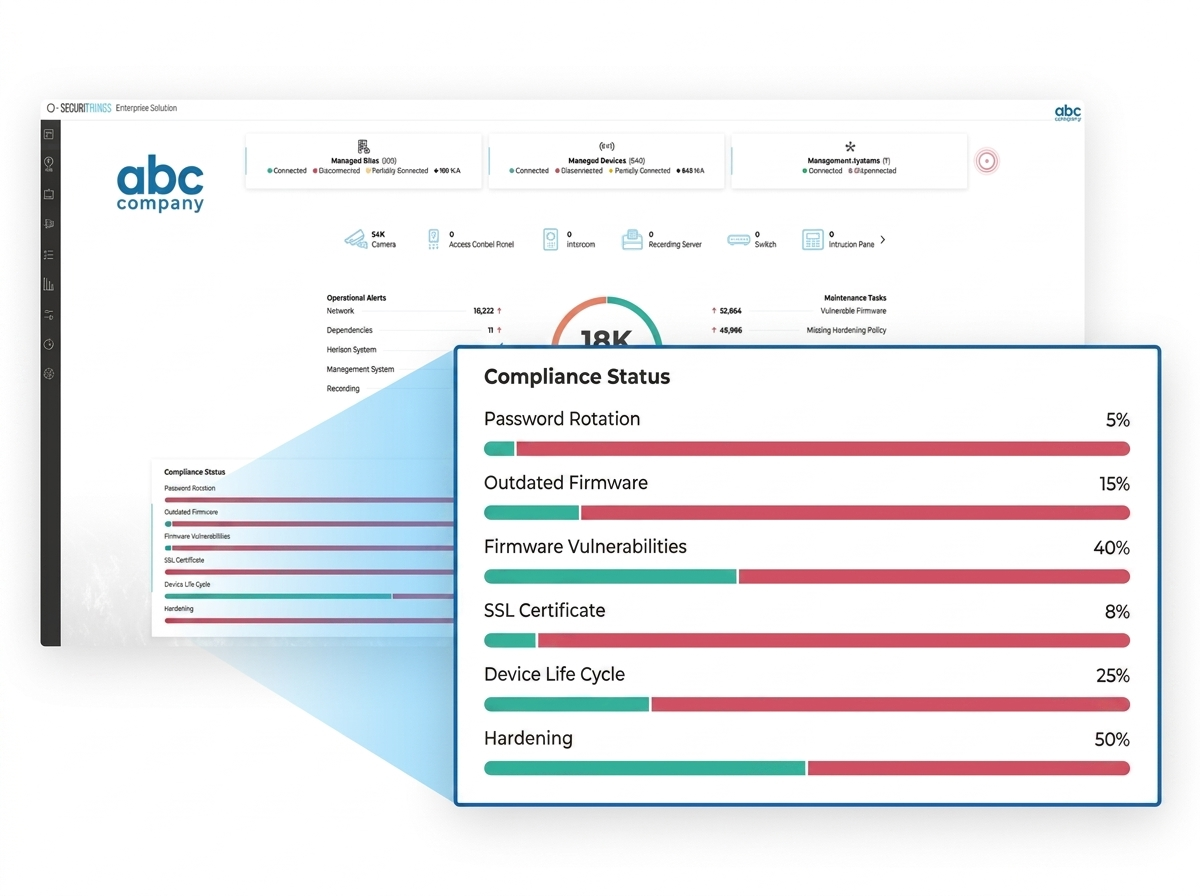
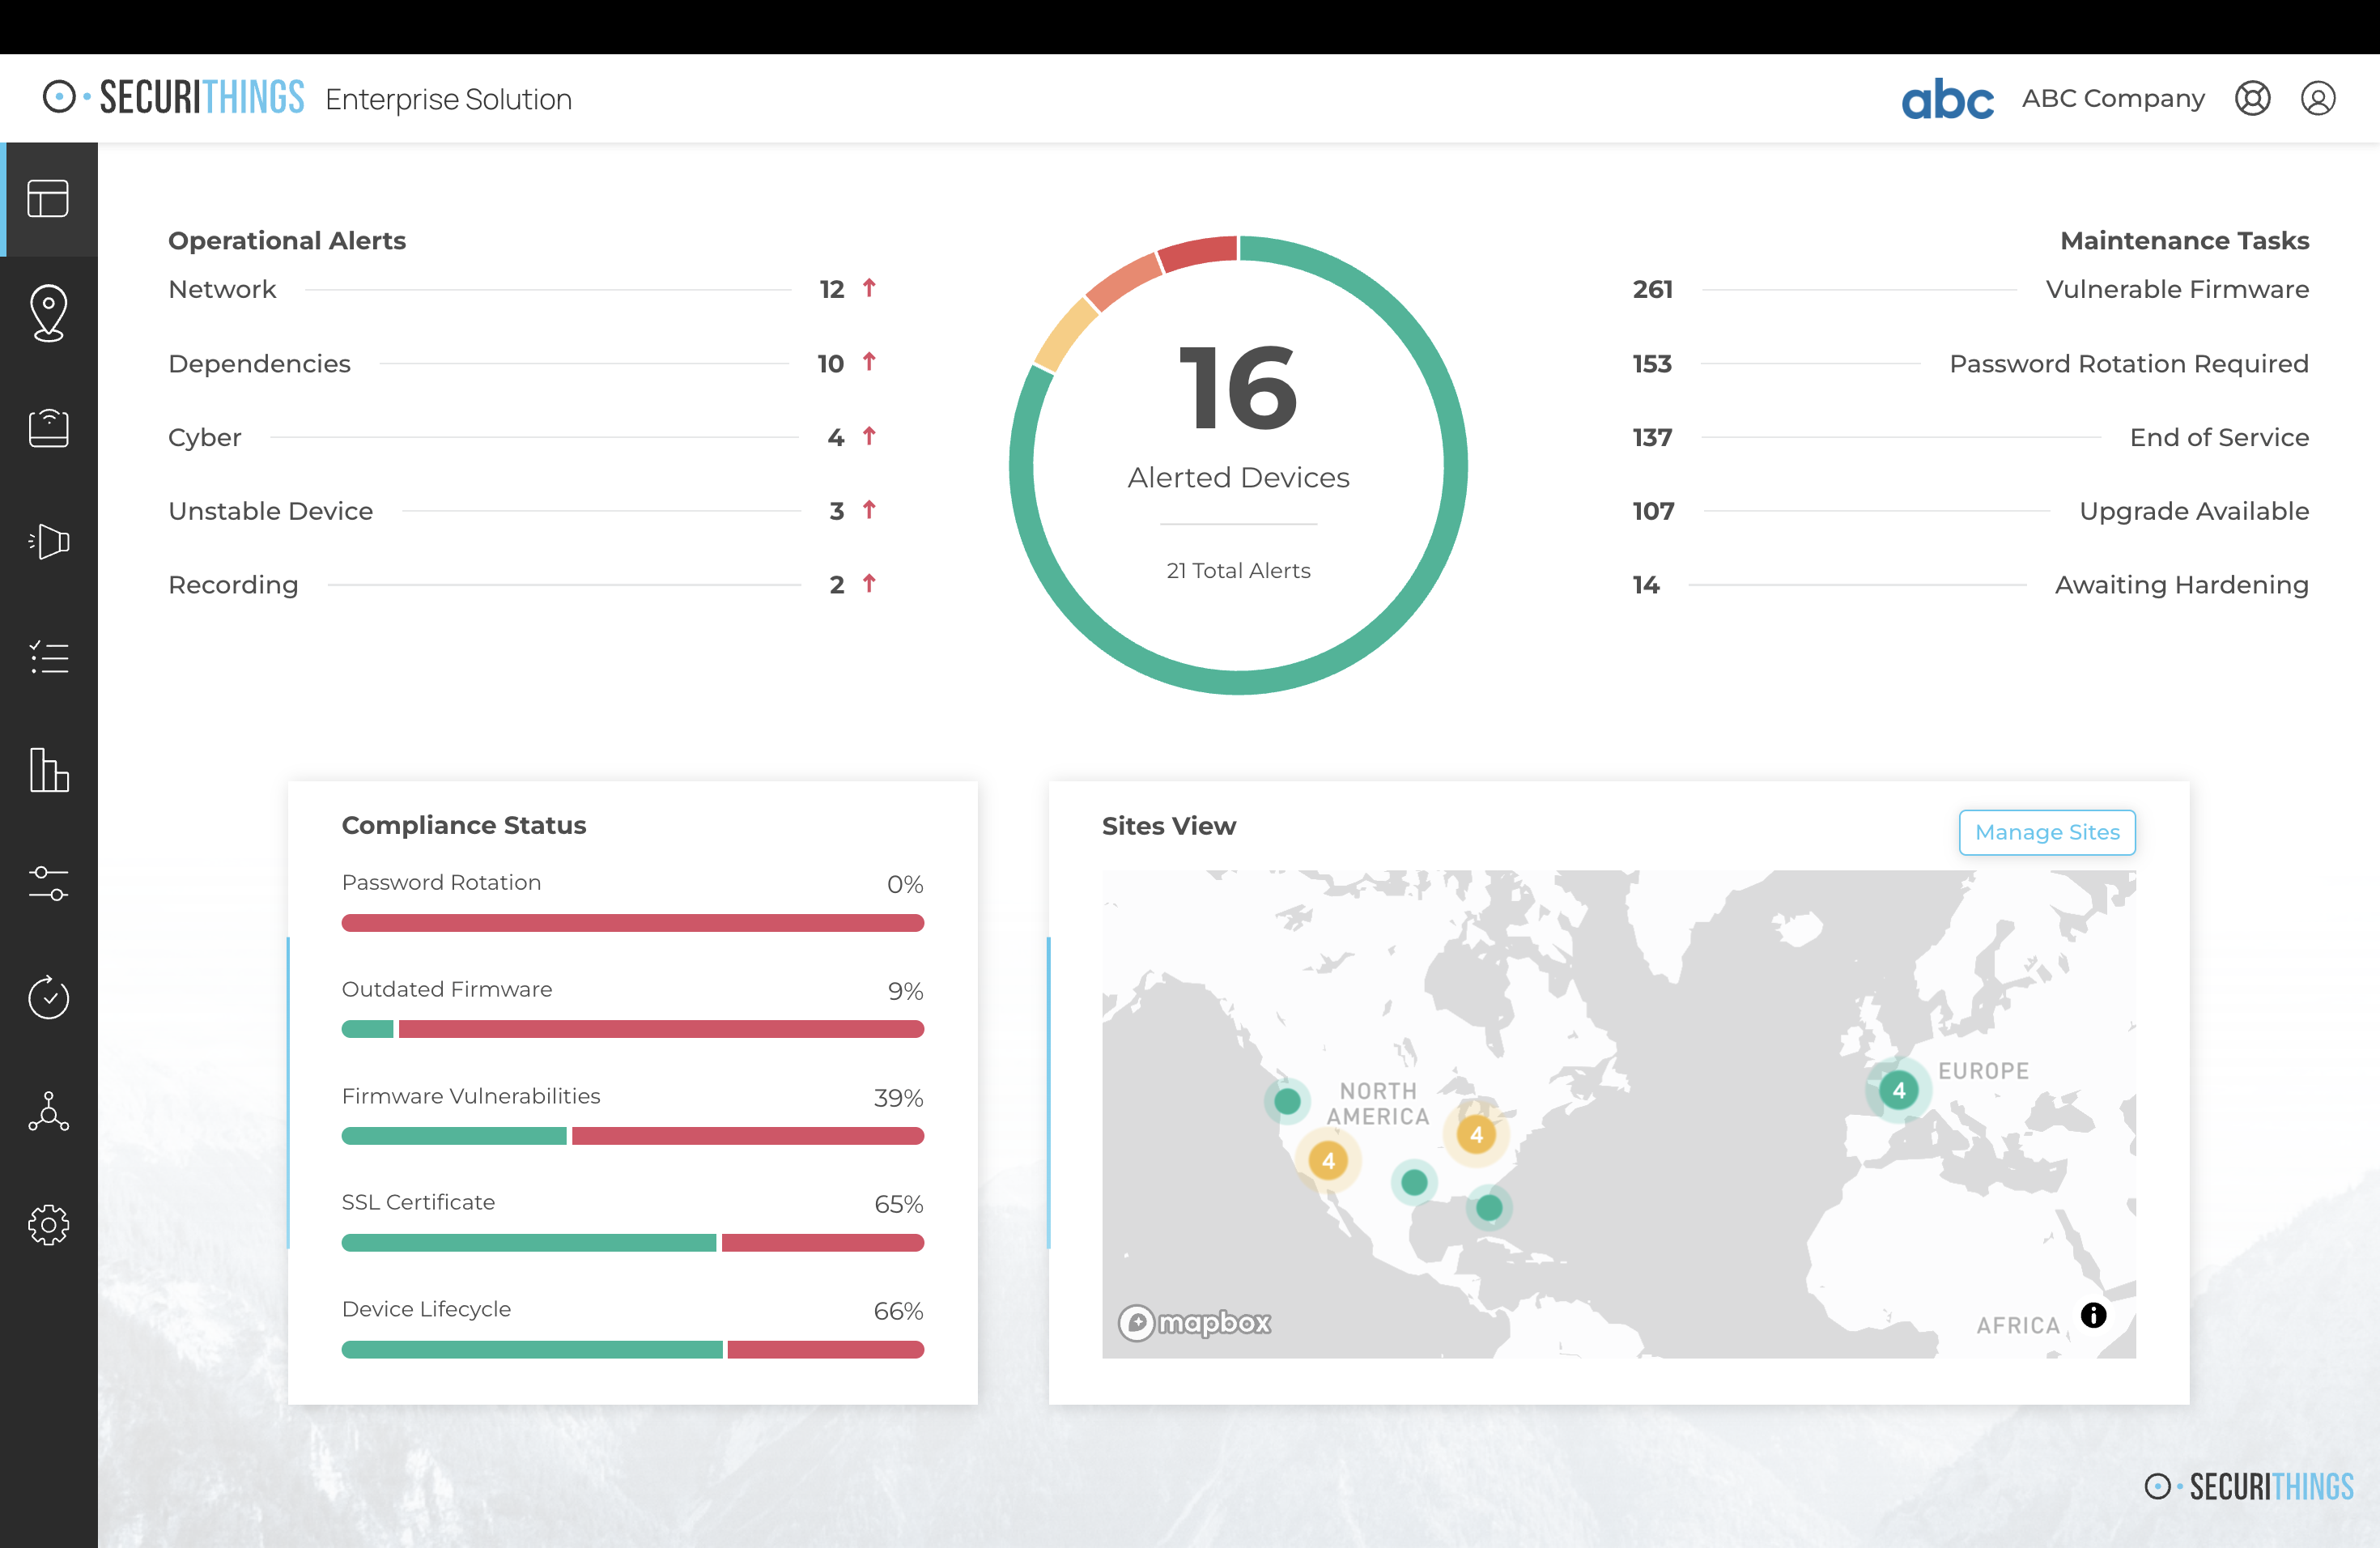
SecuriThings maps device state against your policies and regulations, across the full estate. One live inventory, so attestation reflects reality, not a manual assembly.
IT and security set the standard. The team running the system, physical security, facilities, or IT, executes on the devices they operate. The platform supports that division, rather than assuming one team owns everything.
NEXT STEP: PLATFORM PREVIEW
See your fleet as it actually is
Upload your device list and we will run it through the platform, mapping real CVEs, EOL/EOS dates, and patch availability against your actual fleet.
- Vulnerability exposure by severity CVE breakdown across your fleet
- Device lifecycle status — EOL/EOS dates mapped to your actual devices
- Patch availability — what's remediable and what isn't
- Executive summary — ready to share with IT and security leadership