PROBLEM: DEVICE VISIBILITY
You cannot manage the device fleet you cannot see.
Enterprise IoT fleets grow install by install, until no one has an accurate count of what is deployed or what condition it is in.
Your fleet was never inventoried in a place you can manage it
You do not have an accurate count of your fleet, and the reasons are structural:
The result: No single system accounts for the whole fleet in a centralized way

That gap shows up in daily operations:
The result: teams react to failures after they happen instead of getting ahead of them.
Visibility is the foundation compliance, cyber remediation, and lifecycle planning depend on.
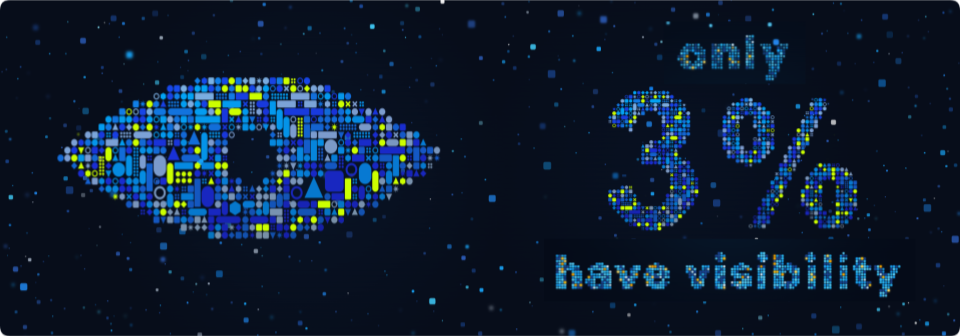
97%
74%
#1
Limited visibility into device status is the #1 barrier to proactively managing device issues like firmware, passwords, certificates, and end-of-life.
From incomplete inventory to continuous fleet visibility
Most teams already know their device inventory is incomplete. This guide covers what to do about it: what visibility needs to cover, how to build it so it stays current, and how to evaluate the tools that claim to provide it.
What’s inside:
- The five dimensions of device visibility, with the risk if each is missing and how to measure it
- A five-step build order for turning VMS, access control, and network data into a live inventory
- Five questions that separate a live, actionable inventory from a one-time device count
- Where visibility is heading, from drift detection to interoperability standards like MCP

The current approaches all share the same structural flaw: they produce a snapshot, not a continuous view.
Point-in-time audits
They're accurate the day they're built. But they get stale within weeks as devices are swapped, reconfigured, or fail silently.
Traditional IT discovery tools
They treat physical security devices as generic network endpoints. For example, they can tell you an IP is responding, not that a camera is degraded, offline, or misconfigured.
Solving device visibility takes more than a scan. It requires:
HOW WE SOLVE IT
Every device. Every site. One continuously updated view.
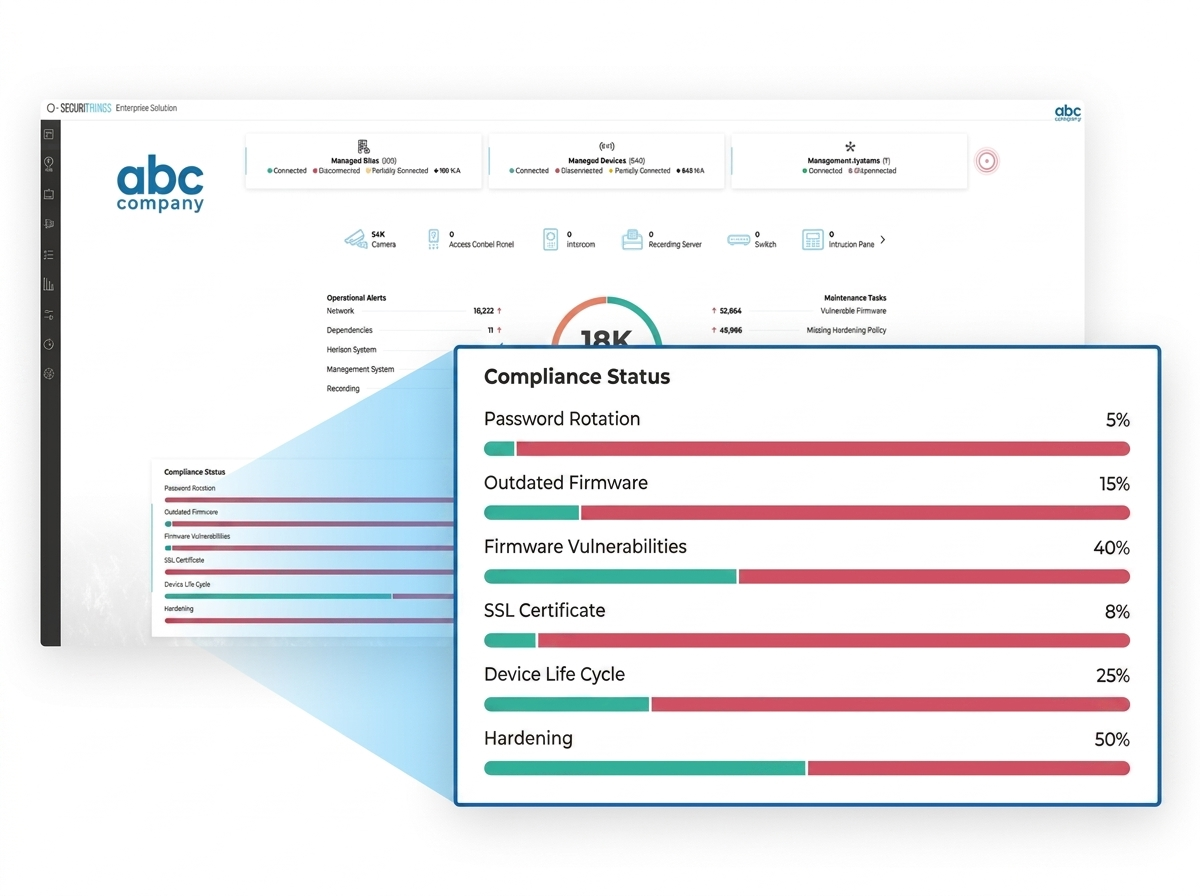
SecuriThings aggregates data from your existing VMS, access control systems, and network sources to build and maintain a live inventory.
You get an accurate, current picture of what's connected and whether each device is working as expected. Nothing gets installed on the individual devices. As devices are added, swapped, or fail, the inventory reflects it.
What it looks like when teams see the whole fleet
"I can finally see my entire fleet, every device, every location. This was impossible before we had SecuriThings."
— Physical security manager
"There is a huge advantage to monitoring all your devices instantly on one page, seeing their status, and delivering reports to your clients, executives, and stakeholders."
— VP, Corporate security
NEXT STEP: PLATFORM PREVIEW
See your fleet as it actually is
Upload your device list and we will run it through the platform, mapping real CVEs, EOL/EOS dates, and patch availability against your actual fleet.
- Vulnerability exposure by severity CVE breakdown across your fleet
- Device lifecycle status — EOL/EOS dates mapped to your actual devices
- Patch availability — what's remediable and what isn't
- Executive summary — ready to share with IT and security leadership